
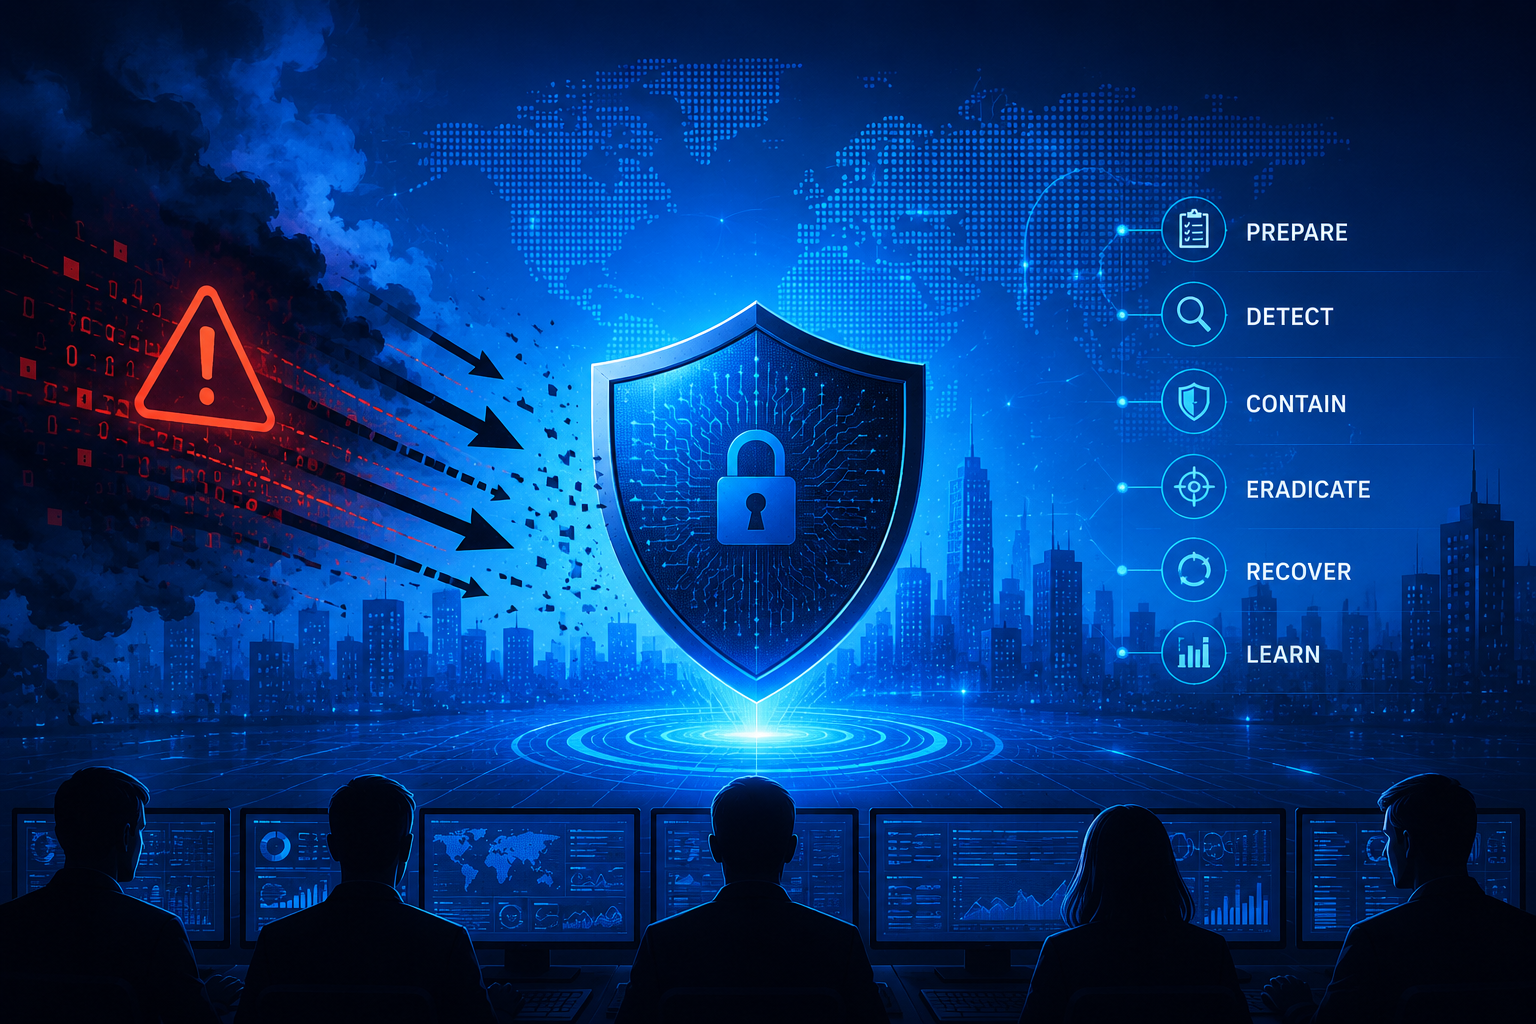
A security incident isn’t a question of ‘if’, but of ‘when’. How organisations can use a structured Incident Response process to minimise damage, meet statutory deadlines and learn from an incident.
What is Incident Response and why is it essential?
Incident Response (IR) refers to the structured process by which an organisation responds to a IT security incident. The aim is to minimise damage, understand the cause, perform recovery on affected systems and learn from the incident.
A security incident can take many forms: a ransomware attack, compromised credentials, a data breach or an unauthorised data transfer by an insider. What all these scenarios have in common is that, without a clear plan, organisations react too slowly, in a disorganised manner or with the wrong measures.
Important: IR is not a purely technical discipline. It encompasses communication, legal considerations, decision-making under pressure and the coordination of internal and external stakeholders.
The 6 phases according to NIST
The NIST Framework is the globally recognised standard for structured Incident Response. It divides the process into six clearly defined phases:
Preparation
Incident Response Plan, CSIRT, playbooks, tabletop exercises – everything that must be in place before an attack occurs.
Detection & Analysis
SIEM, EDR, triage. Assess severity, determine the attack vector, identify systems.
Containment
Isolate systems without destroying evidence related to forensics. Enable network segmentation.
Remediation
Completely remove malware, backdoors and vulnerabilities. No shortcuts.
recovery
Restore from validated backups, phased roll-out, enhanced Monitoring.
Follow-up
Lessons learnt, documentation, updating the Incident Response Plan, informing the relevant public authorities.
The most common mistakes in an emergency
Even well-organised companies make avoidable mistakes when under pressure. Be aware of these and plan accordingly:
- Reinstalling systems immediately: without a backup of forensics, evidence will be lost that is indispensable for root cause analysis and legal action.
- Communicating via compromised channels: If attackers have access to email or Slack, they will be reading your messages. Define an external emergency channel in advance.
- No escalation model: Who decides when a system should be isolated? Without clear authorisation, costly delays will arise.
- Paying a ransom without a strategy: This neither guarantees the return of data nor prevents its publication. Seek legal advice.
- Untested backups: Backups without restore tests will fail in an emergency. Regular testing is not an option, but a requirement.
- Communicating externally too soon: Statements made before the analysis is complete create liability risks and provide attackers with clues.
Regulatory obligations: specific deadlines
Anyone experiencing a security incident faces more than just a technical problem. The reporting obligations apply regardless of whether the incident becomes public:
- GDPR Art. 33: Report to the competent data protection authority in the event of a data breach, deadline
72 Stunden - GDPR Art. 34: Notification of data subjects in the event of a high risk, deadline
unverzüglich - NIS2 early warning: Initial report of significant incidents to the BSI, deadline
24 Stunden - NIS2 full report: Complete report with analysis and measures to the BSI, deadline
72 Stunden
Under NIS2, the absence of a documented Incident Response process carries the risk of a fine of up to 10 million euros or 2 per cent of global annual turnover, in addition to the actual damages.
What organisations should do now
Draw up an Incident Response plan and keep it up to date
Clear roles, escalation procedures, contact lists and checklists for each phase. Must be updated immediately in the event of changes to the infrastructure or staffing.
Define an external emergency communication channel
A dedicated SIM card, an encrypted external app or similar – a communication channel that does not run via the company’s infrastructure, which may have been compromised.
Store backups in isolation and test them regularly
Offline or isolated from the network; otherwise, they will be encrypted along with the rest of the data in the event of a ransomware attack. Carry out restore tests at least quarterly.
Conduct tabletop exercises
Run through a realistic attack scenario, led by a facilitator, at least once a year. Identify gaps in the plan before an attacker exploits them.
Agree on a retainer in advance
Searching for external support during an active attack takes hours. A retainer ensures prioritised availability and a partner who is already familiar with the environment.
Document reporting procedures
Contact details for the BSI, data protection authorities, law enforcement and a specialist solicitor must be included in the plan – they must not have to be looked up when an emergency arises.
Mint Secure GmbH
How Mint Secure supports you
As a specialist IT security service provider, we support organisations across the entire maturity spectrum, from the initial vulnerability assessment right through to assistance during an ongoing incident.
Incident Response
Active incident response with guaranteed response times. Containment, forensics and full recovery by our specialist team.
Penetration Testing
Realistic attack simulations on your infrastructure. Identifying attack vectors before a real attacker can exploit them.
Ransomware Emulation
Testing how far a ransomware attack would progress within your environment and clearly demonstrating where detection and response need to be improved.
IR Consulting & Planning
Bespoke Incident Response plans, scenario-specific playbooks and tabletop training for your team.
Ready to get started? We offer a free initial consultation. Get in touch.
Conclusion
A cyber attack is not a rare occurrence, but a matter of time.
Those who are prepared, understand the key stages, avoid preventable mistakes and keep track of the reporting deadlines under the GDPR and NIS2 will weather an incident with significantly less damage.
Mint Secure supports you every step of the way, from planning through to active incident response. Talk to us.


