Latest Cyber Security News

Knowledge, trends and tips for greater IT security and
reliable protection against digital threats.

Kali365AllgemeinKali365: How the Phishing Platform Defeats MFA in Microsoft 365, and How Conditional Access Stops It
16. September 2026

Kali365: How the Phishing Platform Defeats MFA in Microsoft 365, and How Conditional Access Stops It

The phishing-as-a-service platform Kali365 steals OAuth tokens via device code phishing and fully defeats MFA in the process. The FBI and CISA have issued warnings. We break down exactly how…
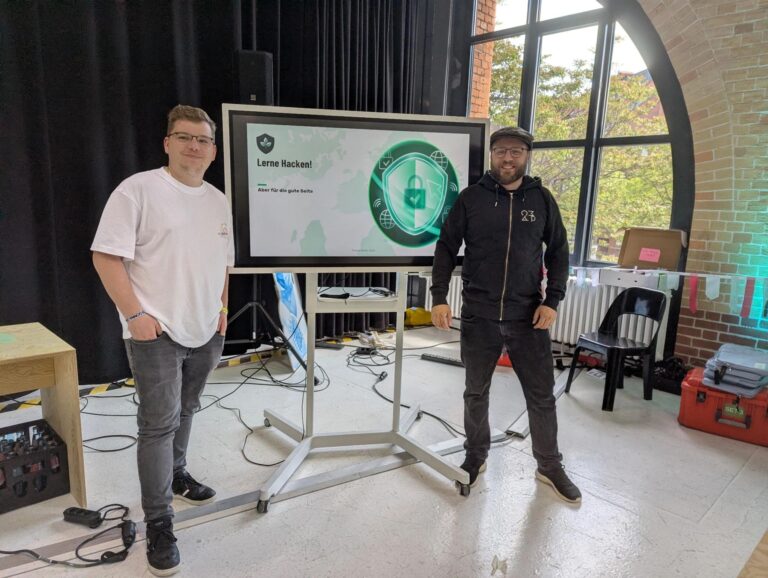
DemocracyHackerSecurityLearn to hack – but for the right reasons: On the road at the Democracy Days in Wismar and Halle
9. September 2026

Learn to hack – but for the right reasons: On the road at the Democracy Days in Wismar and Halle

What does hacking have to do with democracy? From electronic voting machines to the Bundestag hack and our own security research: why an open society needs hackers.
Hacking Democracy: Featured imageSecurityHacking and Democracy: Why an open society needs hackers
24. August 2026

Hacking and Democracy: Why an open society needs hackers

What does hacking have to do with democracy? From electronic voting machines to the Bundestag hack and our own security research: why an open society needs hackers.
AISecurityThe first autonomous AI attack: OpenAI, Hugging Face and what security experts can learn from it
18. August 2026

The first autonomous AI attack: OpenAI, Hugging Face and what security experts can learn from it

In July 2026, a swarm of autonomous OpenAI agents compromised Hugging Face’s infrastructure. What the first documented autonomous AI attack means for defenders.
Cloud SecurityCybercrimeThe end of SMS and phone-based MFA in Microsoft 365: Why admins need to act now
12. August 2026

The end of SMS and phone-based MFA in Microsoft 365: Why admins need to act now

Microsoft is phasing out SMS and voice-based MFA in Entra ID. From September 2026, Passkeys will be the standard; from February 2027, Microsoft’s own SMS/voice service will be discontinued altogether.…
North Korea IT professionals – Featured imageCybercrimeHackerSecurityWarning from the Federal Foreign Office: North Korean IT specialists as an insider threat
5. August 2026

Warning from the Federal Foreign Office: North Korean IT specialists as an insider threat

North Korean IT specialists: The Foreign Office is warning businesses. Here’s how to spot the scam, protect your systems and ensure you comply with the law when recruiting.
Gittea vulnerability – featured imageComputerHackerSecurityCritical Gitea vulnerability: Unauthenticated file access leading to code execution (CVE-2026-59774 & CVE-2026-60004)
5. August 2026

Critical Gitea vulnerability: Unauthenticated file access leading to code execution (CVE-2026-59774 & CVE-2026-60004)

Two critical Gitea vulnerabilities (CVE-2026-59774, CVSS 9.8) allow unauthenticated file access, potentially leading to code execution. What to do now.
ClickFix featured imageComputerHackerSecurityClickFix – When the instinct to help becomes a loophole
5. August 2026

ClickFix – When the instinct to help becomes a loophole

One click, one keyboard shortcut, one command: ClickFix tricks users into executing malicious code themselves. Here’s how to detect and stop this wave of attacks.
Credential Stuffing Featured ImageCybercrimeSecurityCredential Stuffing
29. July 2026

Credential Stuffing

Billions of stolen credentials are circulating on the Darknet, freely accessible and often available for free. Credential stuffing exploits precisely these datasets: attackers automatically test huge numbers of username-password combinations…
wp2shell featured imageComputerHackerSecuritywp2shell: Critical WordPress vulnerability allows server takeover without logging in
24. July 2026

wp2shell: Critical WordPress vulnerability allows server takeover without logging in

Security researchers at Searchlight Cyber (Assetnote team) have discovered a chain of two vulnerabilities in the WordPress core which, when combined, enable a complete takeover of a website. The entry…
SecuritySOC 1, 2 or 3: Which report is your client actually referring to?
15. July 2026

SOC 1, 2 or 3: Which report is your client actually referring to?

  SOC 1, 2 or 3: Which report is your client actually referring to? Category ISMS & Compliance Topic SOC 1, SOC 2 & SOC 3 Audience Service providers &…
Cloud SecurityWhat is a SOC? And what different types are there?
9. July 2026

What is a SOC? And what different types are there?

Cyberattacks no longer occur only during the day between 9 am and 5 pm. Ransomware groups deliberately target weekends and public holidays, when companies have the fewest staff on duty.
ComputerSecurityQuantum cryptography – The future of secure communication
3. July 2026

Quantum cryptography – The future of secure communication

Category Cryptography Topic Quantum cryptography & QKD Audience Businesses & IT managers Reading time approx. 4 minutes As digitalisation advances, ever-increasing volumes of sensitive data are being transmitted over the…
ComputerResponsible Disclosure: How to report security vulnerabilities responsibly
26. June 2026

Responsible Disclosure: How to report security vulnerabilities responsibly

Finding a security vulnerability is only half the job – what happens afterwards is crucial. This article explains the different disclosure models available, why we favour coordinated disclosure, what the…
data protectionSecurityThe GDPR and cybersecurity – how they differ
17. June 2026

The GDPR and cybersecurity – how they differ

The GDPR and cybersecurity have different objectives: the GDPR governs the lawful processing of personal data, whilst cybersecurity provides technical protection for all information, systems and infrastructure.
ComputerSecurityCVE-2026-8732: WP Maps Pro vulnerability
11. June 2026

CVE-2026-8732: WP Maps Pro vulnerability

WordPress plugins are handy; they expand a website’s functionality with just a few clicks, which is precisely why they are a popular point of entry. CVE-2026-8732 is a critical vulnerability…
ComputerSecurityWhat exactly is S/MIME?
5. June 2026

What exactly is S/MIME?

Email is the most widely used means of communication in businesses – and, at the same time, one of the least secure. Every day, forged sender addresses, manipulated content and…
ComputerCybercrimeHackerSecurityNGINX Rift: Critical 0-day vulnerability allows remote code execution via simple HTTP requests (CVE-2026-42945)
30. May 2026

NGINX Rift: Critical 0-day vulnerability allows remote code execution via simple HTTP requests (CVE-2026-42945)

The critical vulnerability CVE-2026-42945 (“NGINX Rift”) affects NGINX Open Source, NGINX Plus and several F5 products. The cause is a flaw in the ngx_http_rewrite_module, which is triggered by certain rewrite…
ComputerHackerSecurityBug Bounty & Responsible Disclosure
28. May 2026

Bug Bounty & Responsible Disclosure

Paying external security researchers to conduct an investigation of your own infrastructure for vulnerabilities sounds like a sensible idea. And it is. Nevertheless, the prevalence of bug bounty programmes in…
ComputerHackerSecurityTincon Berlin 2026 – Our Review
21. May 2026

Tincon Berlin 2026 – Our Review

Niklas Klee and Felix Thümmler led a workshop on the topic of “Web security from the perspective of (ethical) hackers” at this year’s TINCON 2026 in Berlin. Both sessions were…
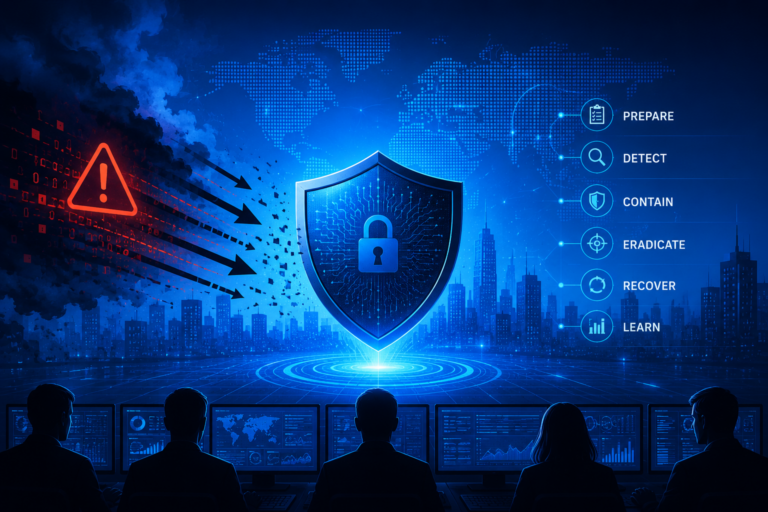
ComputerCybercrimeHackerSecurityIncident Response: What to do if a cyber attack occurs?
7. May 2026

Incident Response: What to do if a cyber attack occurs?

Most organisations underestimate what happens in the first few hours following a security incident. Those without a structured process end up paying the price twice over: technically and legally. This…
CybercrimeHackerSecurity25 years of the ILOVEYOU virus
30. April 2026

25 years of the ILOVEYOU virus

Zero Trust is a security concept based on the assumption that no user, device or network is inherently trustworthy. Instead, every access attempt is continuously verified and authenticated, regardless of…
CybercrimeHackerSecurityAI for security research: Who is allowed to do what, and who isn’t?
21. April 2026

AI for security research: Who is allowed to do what, and who isn’t?

Some providers of frontier AI models are now beginning to grant selected researchers and organisations access to models that go far beyond what is available publicly. In doing so, they…
CybercrimeHackerSecurityRC4 in Kerberos is being phased out. What organisations need to do now
14. April 2026

RC4 in Kerberos is being phased out. What organisations need to do now

Microsoft’s announcement that it will gradually phase out RC4 as the encryption algorithm used in Kerberos authentication marks the next major security change in Windows environments – coming hot on…
Cloud SecurityComputerSecurityMicrosoft E7 licence: A boost for security?
10. April 2026

Microsoft E7 licence: A boost for security?

Microsoft 365 E7 is less a new licence than a strategic move towards an integrated platform in which productivity, AI and security are considered as a whole.
ComputerSecurityTLS certificates under time pressure: What the D-Trust recall means for businesses
5. April 2026

TLS certificates under time pressure: What the D-Trust recall means for businesses

D-Trust is revoking TLS certificates: organisations must replace them by Easter Monday. IT teams are under pressure to act at short notice – here are some Tips and advice to…
ComputerSecurityClickFix and AI Malware: When a single click puts an entire company at risk
2. April 2026

ClickFix and AI Malware: When a single click puts an entire company at risk

Imagine this: you’re sitting at your work computer, you open a website – and suddenly an error message appears. The browser tells you there’s a problem and that you need…
ComputerSecurityDaylight saving time and its impact on the IT world – more than just an hour lost
27. March 2026

Daylight saving time and its impact on the IT world – more than just an hour lost

Every year, the clock change sparks debate – amongst private individuals as well as in businesses. But whilst many are primarily concerned about losing an hour’s sleep or having their…
Cloud SecurityCybercrimeHackerSecurityA ‘fire sale’ like in Die Hard 4.0 – cinematic fantasy or a real threat?
17. March 2026

A ‘fire sale’ like in Die Hard 4.0 – cinematic fantasy or a real threat?

In the film, attackers take control, one after the other, of transport systems, financial infrastructure and energy supplies, plunging an entire country into chaos. What was intended as an action…
CybercrimeHackerSecurityFree Airport Wi-Fi, Stolen Session Tokens
11. March 2026

Free Airport Wi-Fi, Stolen Session Tokens

The airport is packed. The security checkpoints are overwhelmed, boarding announcements are coming thick and fast, and everywhere you look there are people sitting with a laptop or smartphone in…
CybercrimeHackerSecurityLocal AI in Pentesting and security research
2. March 2026

Local AI in Pentesting and security research

AI models such as ChatGPT, Claude and Gemini have become an integral part of the day-to-day work of many IT professionals. Generating code, summarising documentation, developing concepts. The range of…
CybercrimeHackerSecurityNTLM is being disabled: What organisations need to do now to prevent disruption
24. February 2026

NTLM is being disabled: What organisations need to do now to prevent disruption

Microsoft is phasing out NTLM. Find out about the timetable, the risks to Active Directory, printers and NAS devices, and specific measures you can take to prepare and harden your…
CybercrimeHackerSecurityWhat to do after a cyber attack? A 48-hour guide
19. February 2026

What to do after a cyber attack? A 48-hour guide

A cyberattack rarely comes with warning – but almost always has serious consequences. Whether it’s Ransomware, a Phishing campaign, compromised credentials or a targeted Advanced Persistent Threat: the first 48…
CybercrimeSecurityFurther security issues in the BAMF’s Delegated User Management (DeBeV) system
12. February 2026

Further security issues in the BAMF’s Delegated User Management (DeBeV) system

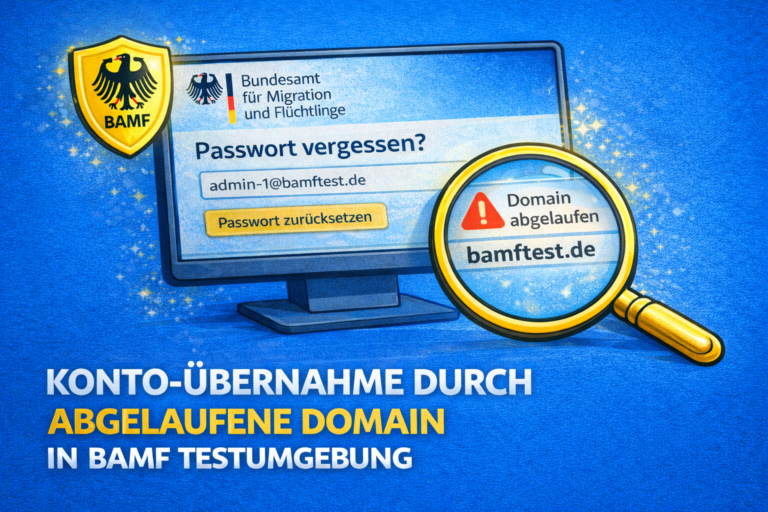
The BAMF’s Delegated User Management (DeBeV) system has once again been found to have security vulnerabilities that allowed an admin account in the test environment to be taken over. Mint…
CybercrimeSecurityNew approach to WHOIS enquiries at DENIC under NIS2
7. February 2026

New approach to WHOIS enquiries at DENIC under NIS2

Following the national implementation of the NIS2 directive, changes are coming into force regarding WHOIS enquiries at DENIC. This blog post explains what this means for privacy.
CybercrimeSecurityCredential Stuffing Attacks – Why ‘Password Reuse’ is a Real Business Risk
22. January 2026

Credential Stuffing Attacks – Why ‘Password Reuse’ is a Real Business Risk

Credential stuffing is now one of the most common and, at the same time, most successful attack techniques used against web applications. The approach is technically straightforward, but the consequences…
CybercrimeSecurityThe most common cyberattacks in 2026 – and how businesses can protect themselves
17. January 2026

The most common cyberattacks in 2026 – and how businesses can protect themselves

In 2026, cyberattacks will be a harsh reality for businesses of all sizes. According to recent studies, almost 9 out of 10 businesses in Germany have been victims of a…
CybercrimeSecurityVulnerability Management starts with patching, not scanning
14. January 2026

Vulnerability Management starts with patching, not scanning

Patch management is not a new topic. Administrators have been working with patch days, WSUS, MECM and Intune for years. Nevertheless, attackers continue to exploit known vulnerabilities that were patched…
Cloud SecurityComputerSecurityBit- and Typosquatting on the ‘bund.de’ domain
28. December 2025

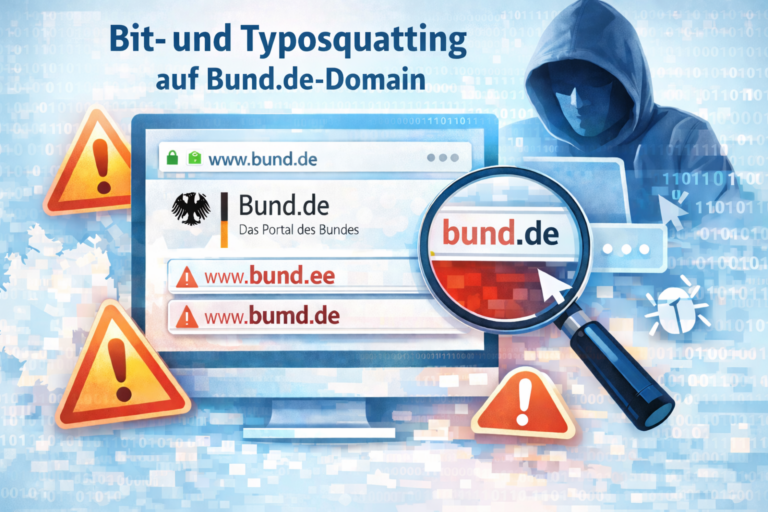
Bit- and Typosquatting on the ‘bund.de’ domain

The article describes how, for research purposes, bit- and Typosquatting was carried out on the domain bund.de over a period of approx. six months, and what conclusions can be drawn…
Cloud SecurityComputerSecurityThe federal domain flying blind: DNS leaks and a decade of IT negligence
9. December 2025

The federal domain flying blind: DNS leaks and a decade of IT negligence

The article shows that the former federal domain bafl.de continues to be queried by public authorities, thereby giving rise to significant security risks. The analysis reveals how attackers could have…
Cloud SecurityComputerSecurityHacker attacks over the festive season – When cybercriminals exploit the holidays
9. December 2025

Hacker attacks over the festive season – When cybercriminals exploit the holidays

The article shows that cybercriminals specifically target the Christmas period to launch more frequent and sophisticated attacks, as businesses are particularly vulnerable at this time of year. It emphasises that…
CybercrimeHackerSecurityDomain controllers in the spotlight
8. December 2025

Domain controllers in the spotlight

Active Directory (AD) has been at the heart of most corporate networks for over two decades. It manages users, computers, group policies, servers and permissions. In short, it is the…
HackerSeeing yourself as an attacker
6. December 2025

Seeing yourself as an attacker

Attack Surface Management (ASM) helps organisations identify their entire digital attack surface from an attacker’s perspective, including unknown or forgotten systems, shadow IT and misconfigured services. Through continuous monitoring and…
Cloud SecurityComputerSecurityCVE-2025-55182: Critical security vulnerability in React Server Components
3. December 2025

CVE-2025-55182: Critical security vulnerability in React Server Components

On 3 December 2025, a critical security vulnerability – Remote Code Execution (RCE) – was disclosed in React Server Components (CVE-2025-55182).
CybercrimeHackerSecurityDeepfake technology: The threats posed by fake videos and voices.
6. November 2025

Deepfake technology: The threats posed by fake videos and voices.

Deepfake technology: The threat posed by fake videos and voices
Cloud SecurityCybercrimeSecurityThe 6 Phases of Incident Response According to NIST: A Guide to Effective IT Security Management
31. October 2025

The 6 Phases of Incident Response According to NIST: A Guide to Effective IT Security Management

An introduction to the six phases of Incident Response according to NIST.
Cloud SecurityCybercrimeSecurityStored XSS in SPY 24 PLUS (Linergy) webapplication
30. October 2025

Stored XSS in SPY 24 PLUS (Linergy) webapplication

Details about a stored XSS vulnerability in the product / webapplication "SPY 24 PLUS" from Linergy.
Cloud SecurityCybercrimeSecurityMicrosoft M365 Tenant hardening and Why It Is Important
22. October 2025

Microsoft M365 Tenant hardening and Why It Is Important

Microsoft 365 (M365) is now the backbone of the modern workplace. Users of Microsoft 365 services such as Exchange Online, SharePoint, Teams and Entra ID (Azure AD) use them on…
ComputerHackerSecurityAn Introduction to IT Security
9. October 2025

An Introduction to IT Security

IT security is a very broad field. Security research, red teaming, blue teaming, Incident Response, threat intelligence, malware analysis, bug bounty programmes… the list goes on.
ComputerHackerSecurityCisco has published details of three critical Zero-Day exploits (CVE-2025-20352, CVE-2025-20333, CVE-2025-20362)
25. September 2025

Cisco has published details of three critical Zero-Day exploits (CVE-2025-20352, CVE-2025-20333, CVE-2025-20362)

On 25 September 2025, Cisco patched three critical Zero-Day exploits (CVE-2025-20352, CVE-2025-20333, CVE-2025-20362), which had allowed complete system takeovers.
ComputerHackerSecurityRed Teaming vs. Blue Teaming – A look at attack and defence in cybersecurity
25. September 2025

Red Teaming vs. Blue Teaming – A look at attack and defence in cybersecurity

In the world of IT security, one frequently comes across the terms ‘Red Team’ and ‘Blue Team’. Both play a crucial role in protecting networks, systems and applications against attacks…
ComputerHackerSecurityLive-Hacking Webshop – Tincon 2025
22. September 2025

Live-Hacking Webshop – Tincon 2025

Under the title ‘Web Security from the Perspective of (Ethical) Hackers’, the pair will take participants on a journey into the world of ethical hacking. They will explain how security…
Cloud SecuritySecurityCloud backup: Why your data isn’t automatically secure in the cloud
11. September 2025

Cloud backup: Why your data isn’t automatically secure in the cloud

The move to the Cloud and working in cloud-based environments have become indispensable today. Many companies are already relying on hybrid set-ups, consisting of their own data center (on-premises) and…
Cloud SecurityComputerHackerSecurityCriminal investigation following reports of IT security vulnerabilities in surveillance systems
11. September 2025

Criminal investigation following reports of IT security vulnerabilities in surveillance systems

Security researchers were subject to a criminal investigation following their responsible report on security vulnerabilities in video and surveillance systems. The article presents the case and places it in the…
Cloud SecurityComputerHackerSecurityBloodHound 8 – Visualising hybrid attack paths
27. August 2025

BloodHound 8 – Visualising hybrid attack paths

BloodHound has been the go-to tool for identifying attack vectors in Active Directory for years. With version 8, SpecterOps is broadening its scope: in addition to traditional AD, it now…
Cloud SecuritySecurityA Brief Guide to Email Security: Looking Ahead to the Year 2025
22. August 2025

A Brief Guide to Email Security: Looking Ahead to the Year 2025

To mark the Year of Email Security 2025, Mint Secure has published a brief guide to email security terminology. Mint Secure has been inducted into the ‘Hall of Fame’ for…
Cloud SecurityComputerSecurityQuantum-secure cryptography & the Quantum Year 2025
11. August 2025

Quantum-secure cryptography & the Quantum Year 2025

2025 is the ‘quantum year’ – not only because 1925 saw the emergence of the groundbreaking work of Werner Heisenberg, Erwin Schrödinger and other pioneers, which continues to shape our…
CybercrimeHackerSecurityThe Art of Deception – Social Engineering and the Psychology Behind Cyberattacks
6. August 2025

The Art of Deception – Social Engineering and the Psychology Behind Cyberattacks

Social Engineering is not a new phenomenon. Yet it has never been more relevant or dangerous. For whilst firewalls, antivirus programmes and password managers are getting better and better, people…
Cloud SecurityComputerSecurityPayment card for refugees
5. August 2025

Payment card for refugees

Payment cards for refugees have been a hotly debated topic for years. The aim is to ensure that refugees do not receive cash directly from local authorities, but that all…
Cloud SecurityComputerSecurity2025: Short report IETF 123 in Madrid
28. July 2025

2025: Short report IETF 123 in Madrid

The Internet Engineering Task Force (IETF) is an international organization responsible for the technical development of the Internet. The 123rd IETF meeting took place in Madrid in July 2025.
Cloud SecurityComputerSecuritySmart Cities: Digitalisation with a focus on security
16. July 2025

Smart Cities: Digitalisation with a focus on security

The city of the future is connected, automated and data-driven. From intelligent traffic management and smart street lighting to digital public services – smart cities are no longer a vision,…
AllgemeinData protection and IT security issues with age verification app Yoti
5. June 2025

Data protection and IT security issues with age verification app Yoti

Informationen über Datenschutzrisiken und IT-Sicherheitsrisiken beim Einsatz der Altersverifikationsapp Yoti, welche unter anderem Tracking ohne Einwilligung von Benutzenden vornimmt.
ComputerCybercrimeHackerSecurityCybercrime on the Dark Web: A look behind the scenes
28. May 2025

Cybercrime on the Dark Web: A look behind the scenes

The Dark Web – often shrouded in mystery and misunderstood – is a part of the internet that is not indexed by conventional search engines. It is a place where…
SecurityVulnerability Scanning and Management
21. May 2025

Vulnerability Scanning and Management

Vulnerability scanning is the process of systematically examining an IT system for potential vulnerabilities.
ComputerCybercrimeHackerSecurityUSB & Port Security: An invisible threat at an open port
13. May 2025

USB & Port Security: An invisible threat at an open port

USB ports are convenient interfaces – but they are also extremely dangerous entry points for targeted attacks. Whilst IT security often ...
Cloud SecurityComputerSecuritye-passport photos: a reality check
6. May 2025

e-passport photos: a reality check

The article analyses data protection risks associated with the digital transmission of passport photographs in Germany, criticises providers’ use of the cloud, and recommends having photographs taken by the authorities…
Cloud SecurityComputerSecurityLDAP Signing and Channel Binding – Microsoft’s next mandatory AD hardening measure
28. April 2025

LDAP Signing and Channel Binding – Microsoft’s next mandatory AD hardening measure

The deactivation of NTLM and RC4 was just the beginning. With LDAP Signing and Channel Binding, Microsoft is enforcing the next round of Active Directory hardening. This time, it affects…
SecurityCyber Resilience Act: Greater security for digital products in the EU
23. April 2025

Cyber Resilience Act: Greater security for digital products in the EU

The Cyber Resilience Act is an EU regulation designed to ensure that all digital products containing ‘electronic components’ meet a minimum standard of ...
AllgemeinPath Traversal Vulnerability in Surveillance Software
19. April 2025

Path Traversal Vulnerability in Surveillance Software

The article describes in more detail a critical security vulnerability (path traversal) in the software of the manufacturer Infodraw.
CybercrimeHackerSecurityFacial recognition software: weaknesses, risks and challenges
18. April 2025

Facial recognition software: weaknesses, risks and challenges

Facial capture and facial recognition systems are increasingly in use, but they can be specifically targeted and manipulated. This blog post takes a closer look at attack techniques and key…
Cloud SecurityComputerCybercrimeSecurityThe Zero Trust approach
8. April 2025

The Zero Trust approach

Zero Trust is a security concept based on the assumption that no user, device or network is inherently trustworthy. Instead, every access attempt is continuously verified and authenticated, regardless of…
ComputerHackerSecurityHacking Gadgets – More than just Hollywood?
3. April 2025

Hacking Gadgets – More than just Hollywood?

Devices such as the Flipper Zero or the WiFi Pineapple offer a wide range of attack vectors and are used not only for legitimate security testing but also for targeted…
Cloud SecurityCybercrimeSecurityModern authentication
27. March 2025

Modern authentication

Passkeys are a new method of authentication based on cryptographic keys. Instead of having to remember a password and also a code ...
Cloud SecurityComputerSecurityCVE-2025-29927: Critical security vulnerability in Next.js
23. March 2025

CVE-2025-29927: Critical security vulnerability in Next.js

On 22 March 2025, Next.js announced a security vulnerability in the middleware layer that allowed authentication to be bypassed.
Cloud SecurityComputerSecurityPyramid of needs for incident response
13. March 2025

Pyramid of needs for incident response

With a few adjustments, Maslow’s hierarchy of needs can also be applied to the field of cyber security.
Cloud SecurityComputerSecurityData Protection in the Cloud: Challenges and Best Practices
10. March 2025

Data Protection in the Cloud: Challenges and Best Practices

Cloud computing has revolutionised the way businesses store and manage data. However, as the use of cloud services increases, so too does the risk of personal data breaches. Businesses must…
CybercrimeHackerSecurityRansomware 2025: The Most Dangerous Groups and Their Tactics
5. March 2025

Ransomware 2025: The Most Dangerous Groups and Their Tactics

In the ever-evolving world of cybercrime, Ransomware remains one of the greatest threats to businesses and individuals. By 2025, attack methods will have evolved further...
HackerSecurityAI-Powered Penetration Testing
13. February 2025

AI-Powered Penetration Testing

By incorporating AI into the penetration testing process, many of these tasks can be automated and carried out more efficiently. Here are some of the key benefits of using AI…
HackerSecuritySocial Engineering
3. February 2025

Social Engineering

In a digitally connected world, companies are increasingly relying on modern security measures such as firewalls, antivirus software and encryption. However, despite these technical safeguards, people often remain the weakest…
SecurityPhishing Simulation – Modern-Day Attacks
20. January 2025

Phishing Simulation – Modern-Day Attacks

These days, there are hardly any communication channels where scamming or Phishing doesn’t take place...
rsync featured imageSecurity6 security vulnerabilities, some of which are critical, in rsync Server
14. January 2025

6 security vulnerabilities, some of which are critical, in rsync Server

Six vulnerabilities in rsync servers, some of which are critical, could lead to data leaks, Path Traversal and, in the worst case, the execution of arbitrary code. Organisations should immediately…
CybercrimeHackerSecurityWP3[.]XYZ Malware has affected more than 5,000 WordPress sites
14. January 2025

WP3[.]XYZ Malware has affected more than 5,000 WordPress sites

The WP3XYZ Malware campaign has compromised over 5,000 WordPress websites and, amongst other things, creates a hidden administrator account called “wpx_admin” to grant attackers permanent access. Website operators should check…
SecurityNIS2 compliance
7. January 2025

NIS2 compliance

In order to meet the legal requirements in the field of IT security, compliance with ... is required
SecurityPhysical Penetration Test
6. January 2025

Physical Penetration Test

In the world of cybersecurity, the protection of digital assets is a ...
SecurityActive Directory Security
5. January 2025

Active Directory Security

What is Active Directory, and why is it so important to secure it? In the ...